

Security
SOC Enrichment With Identity Events
Send your tenant's identity activity straight to your security operations tools.
Integrations · Security
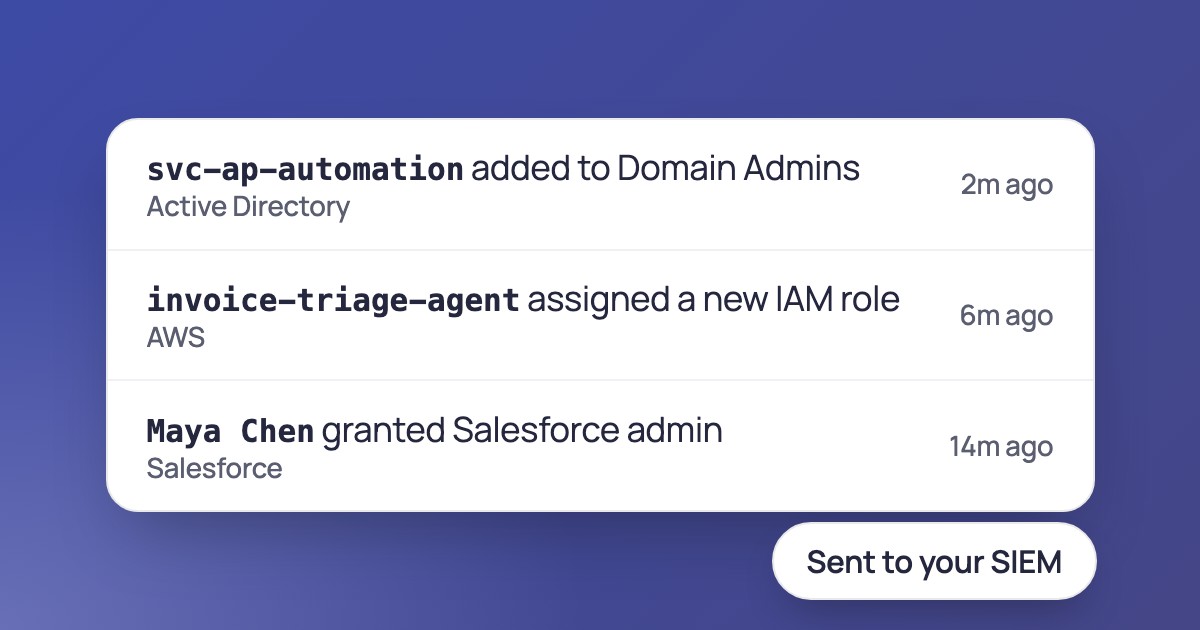
Privileged changes, AI agent permission changes and Hydden risk findings now reach SentinelOne as alerts your analysts can act on.
Most SIEM identity content stops at the login. The events that decide how bad an incident is, like a privileged group add, a role grant or an AI agent gaining a permission, stay in the governance tool while the analyst works somewhere else.
Hydden already knows which identities are privileged, which AI agents they own and how far each one can reach. It now sends that to SentinelOne, with dashboards, detections and response workflows built for the people who work incidents.
Analysts see who an identity is and what it can reach on the alert itself, so triage starts with the answer instead of a search in another tool.
Account changes, privileged grants, AI agent activity and Hydden findings stream into SentinelOne.
Privileged changes and Hydden findings become alerts in the same queue as everything else.
Check blast radius from the alert, then contain the account only after an explicit yes.
Available to all Hydden customers who run SentinelOne AI SIEM. Your Hydden contact can walk you through connecting the two.
Need configuration detail? Technical documentation is available to customers after sign-in.
Let's say John, a security admin, has connected Hydden to his identity stack, and his SOC runs SentinelOne. SentinelOne flags that one of his users has been phished. Here is what Hydden does.
Security
Send your tenant's identity activity straight to your security operations tools.
AI agents
Your AI agents can query the identity record and act on it, within the roles you grant.
NewAI agents
See every AI agent, what it has done, and how much any identity can reach.
Request a trial and see Hydden events in your SOC.